GDB was lying. Daniel Mangum, debugging the Cortex-M33-based nRF54LM20, found that standard GDB memory reads using the 'x' command returned stale cached values after write operations, making successful writes appear to have failed.
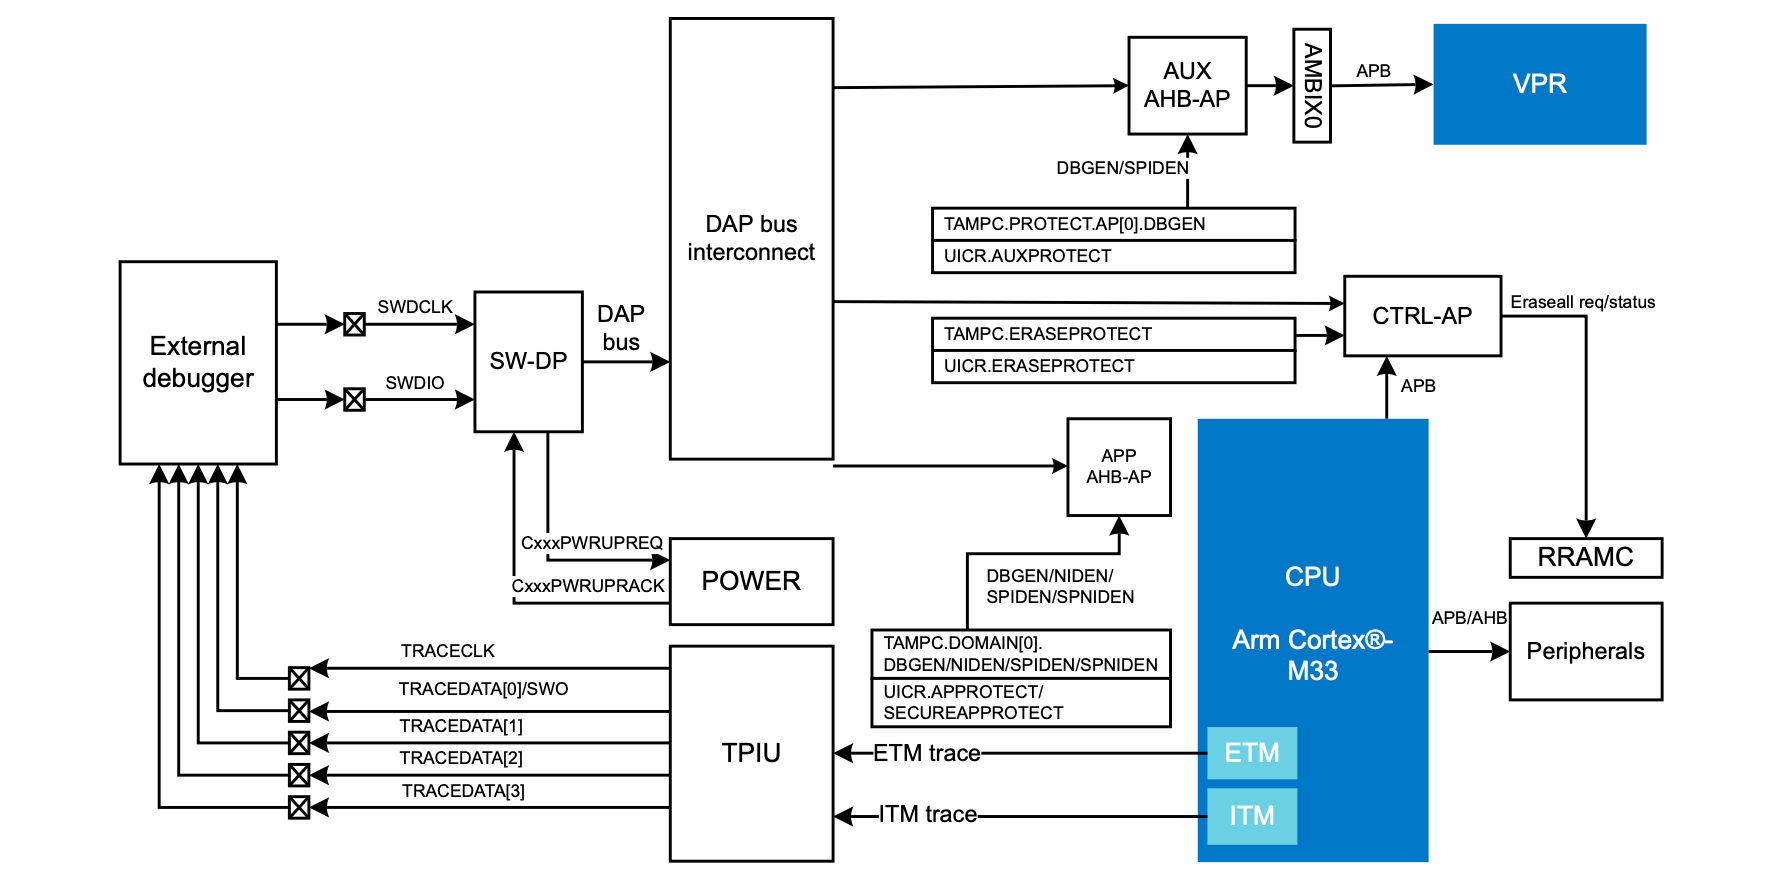
The fix is surgical: bypass the cache by issuing a ReadMemAP command directly to the AHB-AP access port via JLinkGDBServer, which returns the actual register state. The culprit is J-Link's own software cache, not the MCU. The full post goes deep into the nRF54LM20's Key Management Unit and cryptographic memory architecture, which is where the stale reads were most dangerous and most confusing.
This matters because silent debugger caching can invalidate your entire debug session without a single error message. Mangum caught it fast and had a workaround. The next engineer might not. Read the original post for the exact command syntax and the KMU internals that made this bug so plausible.
[READ ORIGINAL →]