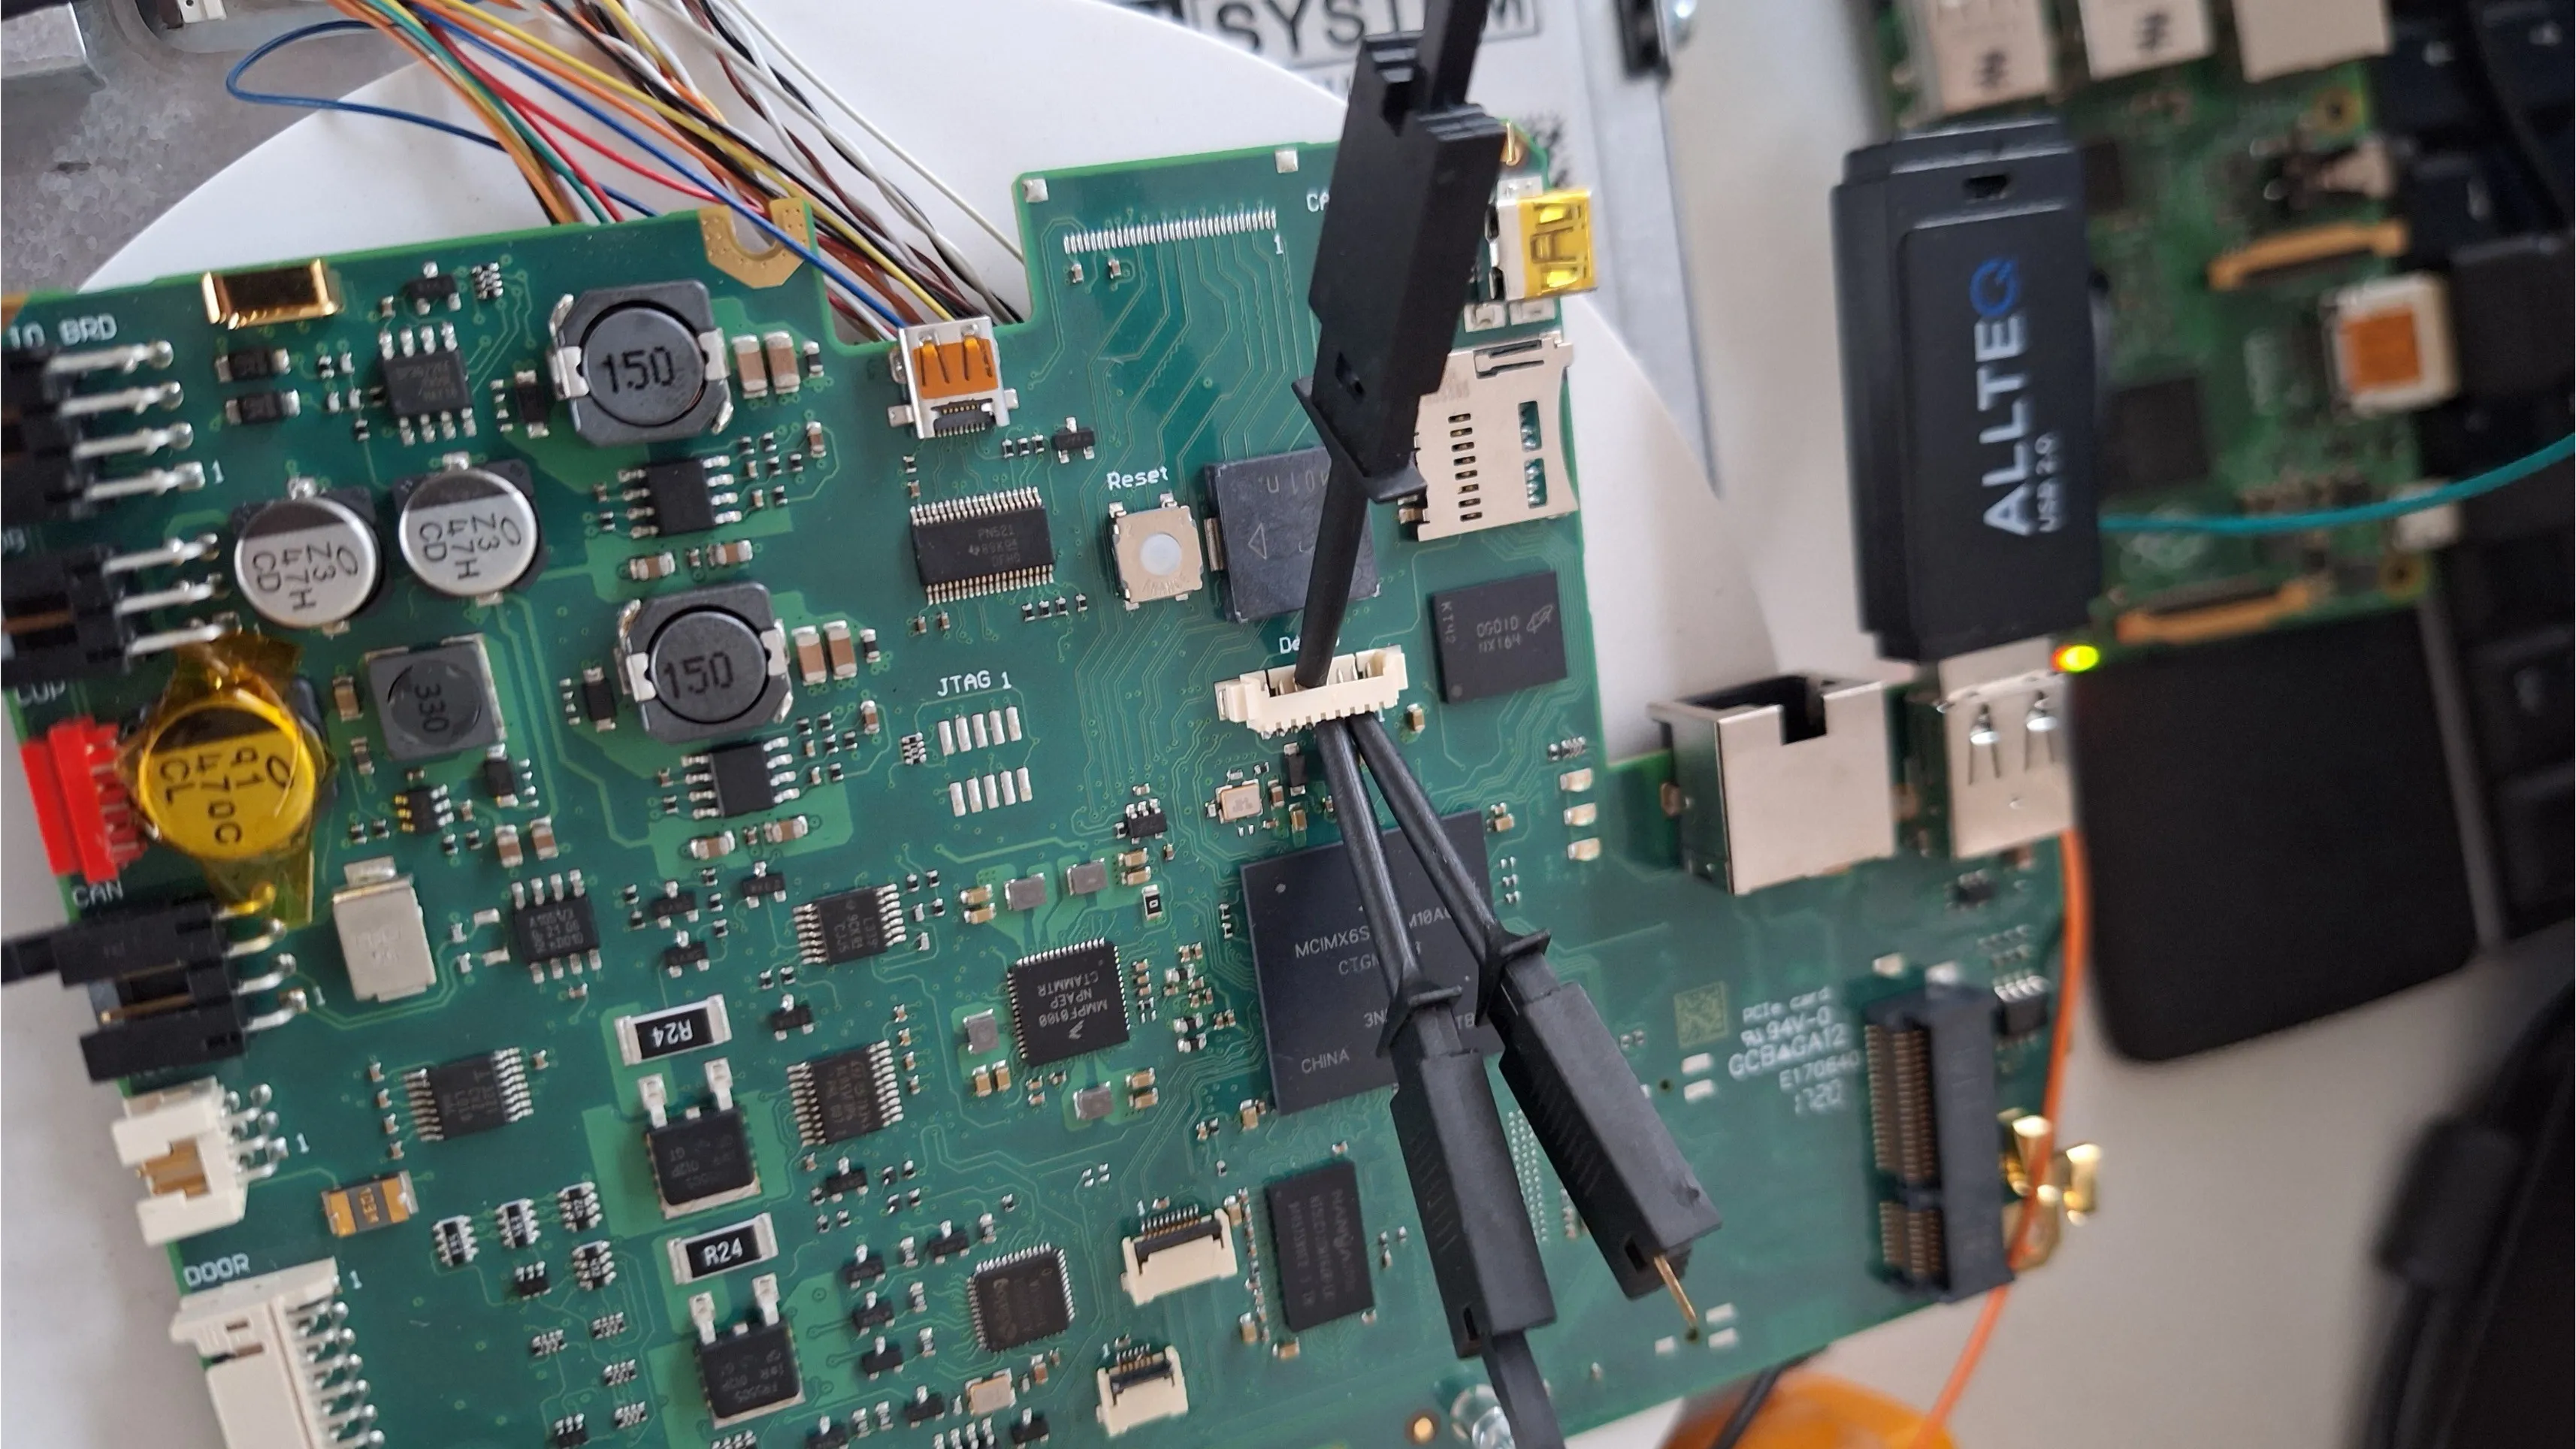
Robin M. got DOOM running on a Spengler PSL50 commercial coffee kiosk, a pay-to-drink smart device built around an i.MX 6 ARM Cortex-A9 processor running a 2013 Linux build.
The entry point was a debug port on the touchscreen module. No uboot password, no protections. A single setnv command dropped Robin into an sh prompt. He compiled fbDOOM, a framebuffer-rendering build, as a self-contained binary to sidestep the 13-year-old system dependencies entirely.
The full write-up at hackaday.io details the pin probing, the console connection, and the compile process. It is worth reading not for the punchline but for how cleanly Robin documents each step of exploiting a completely unprotected embedded Linux device that ships in public-facing commercial hardware.
[READ ORIGINAL →]